NEWS
Apache HTTP/2 Flaw Leaves Distros Without a Patch
Apache 2.4.71 patches a 9.8 HTTP/2 race, yet Debian, Amazon Linux, and an archived GitHub module have no fix, and vendors split on exploits.

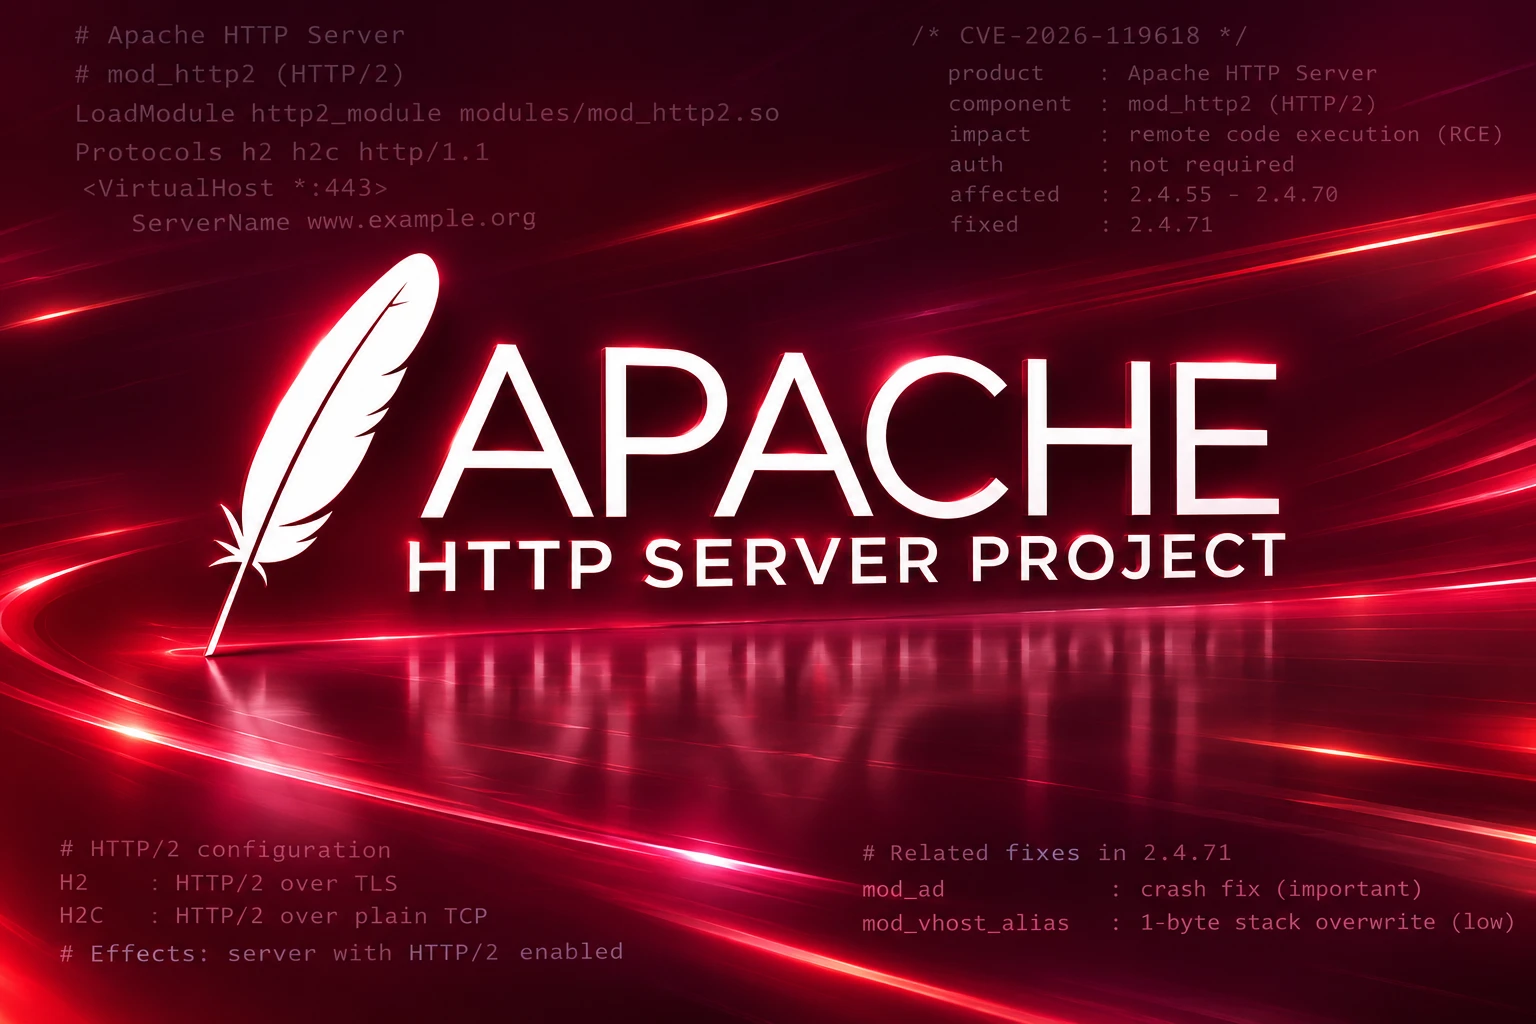
Apache HTTP Server 2.4.71, released November 11, 2026, patches CVE-2026-119618, a critical HTTP/2 race that can let a remote attacker run code with no login. The hole sits in mod_http2 on versions 2.4.55 through 2.4.70. Upstream is closed. A long tail of Debian stables, Amazon Linux, and a locked GitHub tree is not.
The finder of record is an AI scanner. The man who used to ship a convenient standalone build of the same module had already frozen that tree, blaming LLM noise. Vendors spent the first day arguing over whether a working exploit even exists.
9.8 on a Server That Speaks HTTP/2
Apache lists heap corruption and RCE in assign_headers as a critical flaw in mod_http2. Two code paths touch a shared resource without a lock, and that race can wreck heap memory in the worker and run code as the server process.
Red Hat, which ships the daemon in Red Hat Enterprise Linux, scored the bug 9.8 on CVSS v3.1 (AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). A remote attacker who can reach the server needs no account. Only hosts that speak HTTP/2 are in the blast radius. Hosts that serve HTTP/1.1 alone are not.
Red Hat’s write-up is blunt about the mechanics. HTTP/2 lets many streams share one connection, and mod_http2 spreads that work across threads. A worker thread can write into memory the connection thread still owns, through a shared lock-free allocator, and that write is enough to corrupt the child process.
THE SCORECARD
- Apache rating: Critical, with no numeric CVSS on the project advisory.
- Red Hat score: 9.8, network, low complexity, no privileges, no user click.
- Weakness: CWE-362, a race on a shared resource.
- Fix: Apache HTTP Server 2.4.71, shipped November 11, 2026, in commit 824beab.
The same 2.4.71 tarball also closes CVE-2026-106023, an important crash in mod_md on 2.4.30 through 2.4.70, and CVE-2026-109163, a low one-byte stack overwrite in mod_vhost_alias on 2.4.69 and 2.4.70. Neither matches the HTTP/2 race in reach.
Anthropic’s Scanner Filed First, Google Followed
Apache credits Anthropic’s OSS Scanner as ANT-2026-MAPKT6MZ, reported October 26, 2026. Anthony Weems and Simon Scannell of Google Cloud Vulnerability Research filed the same bug on November 3. Eric Covener of the Apache HTTP Server Project posted the oss-security note at 12:19 UTC on November 11, tagged severity critical, the same day the 2.4.71 tarball landed. That is 16 days from the first report to the public fix.
Anthropic had opened an opt-in scanner for open-source projects on October 8, 2026, modelled on Google’s OSS-Fuzz. The company said reports from that service are fully model-generated, with no human review or triage, and that each one is supposed to carry a reproducer, a note on when the bug entered the tree, and a candidate patch when one exists. Eighteen days after that launch, the scanner had a 9.8-class race in the web’s most deployed server.
FROM ARCHIVE TO 2.4.71
- June 9, 2026: Stefan Eissing archives the standalone mod_h2 GitHub tree as read-only, with v2.0.42 as the last tag.
- October 8, 2026: Anthropic opens OSS Scanner as a free, model-only audit for opted-in projects.
- October 26, 2026: The scanner reports ANT-2026-MAPKT6MZ to the Apache security team.
- November 3, 2026: Weems and Scannell report the same assign_headers() race.
- November 11, 2026: Apache lands 824beab, ships 2.4.71, and Covener posts the public notice.
Google’s filing did not change the patch. It confirmed that two independent groups, one of them an automated model pipeline, had both walked into the same unlocked table in h2_request.c.
Why Stefan Eissing Locked the GitHub Door
Stefan Eissing archived the standalone mod_h2 repository on June 9, 2026, writing that the module now lives inside Apache httpd and that “LLM craziness” left him without time to keep a separate GitHub tree. The last GitHub tag is v2.0.42, released May 29, 2026, which Apache lists as affected, and no fixed standalone release exists.
That GitHub tree was the extra-convenient channel. Official mod_http2 has shipped inside httpd since 2.4.17. The GitHub copies, tagged 2.0.8 through 2.0.42, were for people who wanted the module faster than the httpd release train. Apache’s advisory still names those builds as affected. The archived standalone HTTP/2 module README is the only remaining guidance, and it is a closed door.
This repository is now archived and no longer maintained. The module lives on as part of the Apache httpd project and is maintained there. The current LLM craziness does not allow me the time and mental resources to keep on providing a separate and for many people more convenient place here.
Stefan Eissing, mod_h2 maintainer, GitHub README
The irony writes itself. Eissing shut the mirror because language models were eating his time. A language-model scanner then found a critical race in the code, and anyone who still loads that GitHub.so has nowhere to pick up a patched tag. Wiz’s own product table even listed a patched mod_h2 line of “2.0.24 and newer,” which collides with the affected range through 2.0.42; the body of that same note tells operators to move past 2.0.42, a tag that does not exist.
Debian, Amazon, and JBoss Have No Fix
People who build httpd from Apache’s tarball can move to 2.4.71 today. Most production boxes do not. They wait on a distro package, an appliance vendor, or a container image that may still vendor the old module.
WHO HAS A FIX AND WHO DOES NOT
| Platform | Status | Fixed package |
|---|---|---|
| Apache HTTP Server project | Fixed | 2.4.71 |
| Red Hat Enterprise Linux 9 | Fixed (Important) | mod_http2-2.0.26-7.el9_9.1 (RHSA-2026:98981) |
| Red Hat Enterprise Linux 10 | Fixed (Important) | mod_http2-2.0.29-5.el10_3.1 (RHSA-2026:98978) |
| RHEL 9.4, 9.6, 9.8 and 10.0, 10.2 streams | Fixed | See each RHSA |
| Red Hat Enterprise Linux 8 and earlier | Not affected | None needed |
| Debian sid | Fixed | apache2 2.4.71-1 |
| Debian bookworm, trixie, forky | Vulnerable | None listed |
| Amazon Linux 2, 2023, 2027 Preview | Pending fix | None listed |
| Red Hat JBoss Core Services, Hardened Images | Affected | None listed |
| Standalone mod_h2 (GitHub) | Affected | None (repo archived) |
Debian’s tracker still marks bookworm at 2.4.68-1~deb12u1 (and the security pocket at 2.4.67-1~deb12u3), trixie at 2.4.68-1~deb13u1 and 2.4.69-1~deb13u1, and forky at 2.4.69-1, all vulnerable. Only sid carries 2.4.71-1. Amazon Linux Security Center lists Amazon Linux 2 Core, Amazon Linux 2023, and Amazon Linux 2027 Preview as pending, with a 9.8 of its own and no advisory date. Ubuntu had no public tracker page for the CVE on November 12, 2026.
JBoss Core Services (jbcs-httpd24-mod_http2) and Red Hat Hardened Images are listed affected with empty errata fields. Those are the copies that never move when a host runs dnf update. A version string on the banner is a poor oracle anyway, because backported packages often keep the old number while the module bits change, and a custom GitHub build can sit beside a patched httpd binary.
Red Hat Split the Severity on Purpose
Red Hat Product Security called the flaw Critical at the CVE level and then rated the RHEL 9 and RHEL 10 advisories Important. The split is not a shrug. Those packages give each HTTP/2 stream its own allocator, which the vendor says makes the race much harder to win. Builds before mod_http2 2.0.8 do not contain the bad code, which is why RHEL 8 and earlier show “Vulnerable Code not Present.”
The same page also says public research has shown a reliable exploit against a default-configured server with mod_http2 enabled. Wiz, posting the same day, said no exploit was available and that no use in the wild had been reported. Those two sentences now travel together in every briefing, and they do not describe the same fact.
WHERE EXPERTS DISAGREE
- Red Hat: Public research has shown a reliable exploit on a default server with mod_http2 on, enough to take the server process.
- Wiz (November 11, 2026): No exploit is available, and no exploitation in the wild has been reported.
Wiz also counted 64% of cloud environments as holding a resource in the affected version range, and 51% as holding a publicly exposed instance. That inventory does not take configuration into account, a caveat the firm printed in the same paragraph. A fleet scan that keys on 2.4.55 through 2.4.70 will light up boxes that never added h2 or h2c. watchTowr, investigating the same day, said the hole looks configuration-specific, with only hosts that enable h2 in Protocols exposed.
The 64% figure is still a real inventory of stale binaries. It is not a count of servers an attacker can race today. Treating it as one is how a version match turns into a fire drill on hosts that still speak HTTP/1.1.
What the Protocols Directive Turns On
HTTP/2 in Apache is off until an admin adds h2 or h2c to the Protocols line, which defaults to http/1.1. The setting can sit in the global config or on a single virtual host, so both must be checked. Removing h2 and h2c is the workaround until a package lands.
Apache’s HTTP/2 guide walks through turning on HTTP/2 via the Protocols directive for the whole server or one name-based host. h2 is HTTP/2 over TLS. h2c is HTTP/2 over plain TCP. A global Protocols http/1.1 with a vhost that still lists h2 leaves that vhost on the bad path. A front-end that strips HTTP/2 can also hide a backend that still accepts it.
HOW TO READ THE CONFIG
- Server-wide line: Search the main config for Protocols and for LoadModule http2_module.
- Every virtual host: A nested Protocols h2 http/1.1 turns the race back on for that name even if the global line is safe.
- Bridge setting: Protocols http/1.1, with h2 and h2c gone, is the workaround Apache did not print and Wiz did.
Apache’s advisory offers no workaround. Wiz told operators who cannot move to 2.4.71 yet to restrict the line to HTTP/1.1. That cut is the only lever Debian bookworm, Amazon Linux, JBoss Core Services, and GitHub-module hosts have until a package appears. It also costs HTTP/2 performance on purpose, which is the point of a bridge, not a destination.
May’s HTTP/2 Fix Left This Code Path Open
This is not the first HTTP/2 memory bug in 2.4.x this year. CVE-2026-23918, a double-free with possible code execution on an early stream reset, hit 2.4.66 and was fixed in 2.4.67 on May 4, 2026. Anyone who moved to 2.4.67, 2.4.68, 2.4.69, or 2.4.70 to close that hole still runs a build this new race affects. A May patch was not a season ticket.
mod_http2 has a longer ledger of stream and header crashes, from RST memory that was slow to return to continuation frames that exhausted RAM. Those were denial-of-service bugs. CVE-2026-119618 is the one Apache marked critical because the broken object is a header table under a worker, and the outcome it names is code execution, not a hung child.
The people who already did the right thing in May are now in the same queue as everyone else: wait for 2.4.71, wait for a distro errata, or take HTTP/2 off the wire. A box that shows 2.4.70 in the banner after a careful spring upgrade is not a success story this week. It is the upper edge of the affected range.
Amazon Linux 2, Amazon Linux 2023, and Amazon Linux 2027 Preview still show pending fix on the vendor tracker, with no advisory date attached. Until those rows move, the Protocols line is the control those hosts actually have.

Xiaomi 18 Pro Goes Global as Its Privacy Filter Falters

iFixit Finds HomeView Glued Shut After Repair Gains

Polymetallic Nodules Shelter 4,139 Animals Miners Want

One UI 9.5 Puts Now Brief Behind a System Agent

Framework’s $99 Keyboard Brings Laptop Repair to the Couch

Microsoft 365 Auth Fault Took Down Exchange and Teams

OpenClaw 2.0 Ships a Team Workplace With Host-Trust Defaults

Xbox Caps Game Pass Cloud Gaming at 15 Hours

OpenAI Unveils GPT-6 Astra With a Critical Cyber Label

Squishy Dumpling Toys Recalled After Hiding Illegal Water Beads
-
 NEWS3 months ago
Microsoft 365 Auth Fault Took Down Exchange and Teams
-
 NEWS3 months ago
OpenClaw 2.0 Ships a Team Workplace With Host-Trust Defaults
-
 GAMING3 months ago
Xbox Caps Game Pass Cloud Gaming at 15 Hours
-
 NEWS3 months ago
OpenAI Unveils GPT-6 Astra With a Critical Cyber Label
-
 LIFESTYLE3 months ago
Squishy Dumpling Toys Recalled After Hiding Illegal Water Beads
-
 BUSINESS3 months ago
Diesel Breaks Its Record as the White House Claims Credit
-
 NEWS3 months ago
IFA 2026’s Weird Gadgets Are Building a Sensor Home
-
 BUSINESS3 months ago
ChargePoint Stock Rally Prices Wilmer’s Three-Year Cash Plan